Category: Windows Server

  • WSUS Not working on Windows Server 2025

    WSUS Not working on Windows Server 2025

    When setting up WSUS on a Windows Server 2025, one might encounter issues with the update of the repository, and the server will never synchronise.

    After looking at the logs, which can be found in the C:\Windows\UpdateLog.log one would see timeout errors.

    First things to check are the firewall and internet access of the server. The other reason why the synchronization would fail it would be due to the security defaults of Windows Server 2025, where TLS and SSL, which are disabled by default.

    For WSUS to work, one needs to enable these protocols. To enable them, one can use applications such as IIS Crypto, which can be downloaded from the link below.

    https://www.nartac.com/Products/IISCrypto/

    After enabling TLS and SSL, reboot the server. After logging in, try to synchronize the WSUS, and it should be working.

  • Fix Remote Desktop Licensing Mode is not configured

    Fix Remote Desktop Licensing Mode is not configured

    Having fully installed Remote Desktop Services (RDS) on a server with the RD Connection Broker and RDS licensing set per user and everything is working with a valid license.

    After some time you notice a popup when you connect saying,

    Remote Desktop licensing mode is not configured
    Remote Desktop Services will stop working in 104 days. On the RD Connection Broker server, use Server Manager to specify the Remote Desktop licensing mode and the license server.
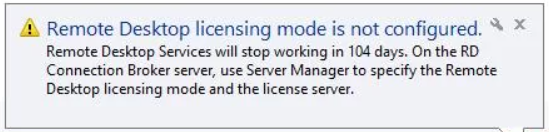
    When you open the RD Licensing Diagnoser, you will be prompted with an error saying, The licensing mode for the Remote Desktop Session Host server is not configured.

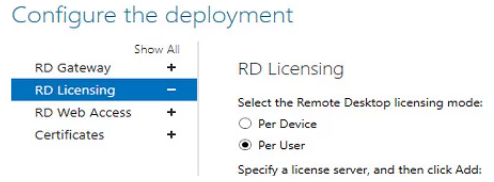
    From the Server Manager under Configure the Deployment and RD licensing, all seem to be configured well.
    Open a PowerShell as Administrator on the server and run the following command

    $obj = gwmi -namespace "Root/CIMV2/TerminalServices" Win32_TerminalServiceSetting
    $obj.GetSpecifiedLicenseServerList()

    This will show a parameter called SpecifiedLicenseServerList which would be empty as below.

    To populate the parameter, use the following command

    $obj.SetSpecifiedLicenseServerList("<full fqdn server name>")

    After this is done, the RD Licensing Diagnoser parameter should not report any errors. It is suggested to restart the server after this change.

    Alternatively, one could do this with registry with the following PowerShell script

    # Specify the RDS licensing type: 2 - Per Device CAL, 4 - Per User CAL
    $RDSCALMode = 4
    $RDSlicServer = "<server full fqdn name>"
    # Set the server name and type of licensing in the registry
    New-Item "HKLM:\SYSTEM\CurrentControlSet\Services\TermService\Parameters\LicenseServers"
    New-ItemProperty "HKLM:\SYSTEM\CurrentControlSet\Services\TermService\Parameters\LicenseServers" -Name SpecifiedLicenseServers -Value $RDSlicServer -PropertyType "MultiString"
    Set-ItemProperty "HKLM:\SYSTEM\CurrentControlSet\Control\Terminal Server\RCM\Licensing Core\" -Name "LicensingMode" -Value $RDSCALMode

  • Fix: Storage Replica warning Events 10448 Storage Replica has failed an application IO

    Fix: Storage Replica warning Events 10448 Storage Replica has failed an application IO

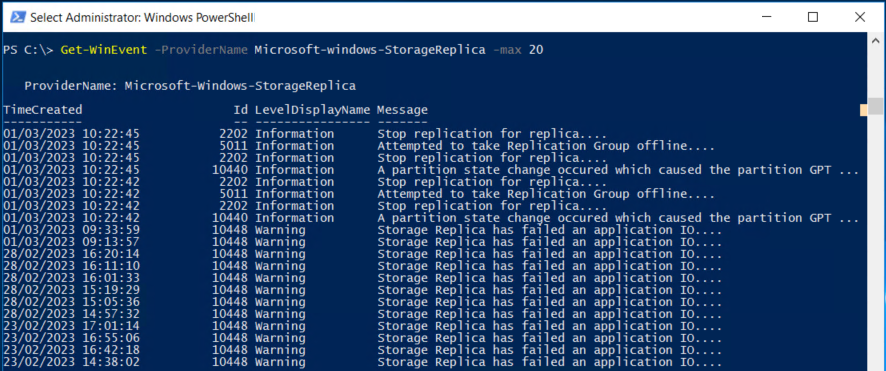
    When checking the logs of the Storage Replica on a Windows Server 2016, 2019 or 2022, using the below command, you get the error saying that Storage Replica has failed an application IO.

    Get-WinEvent -ProviderName Microsoft-Windows-StorageReplica -max 20

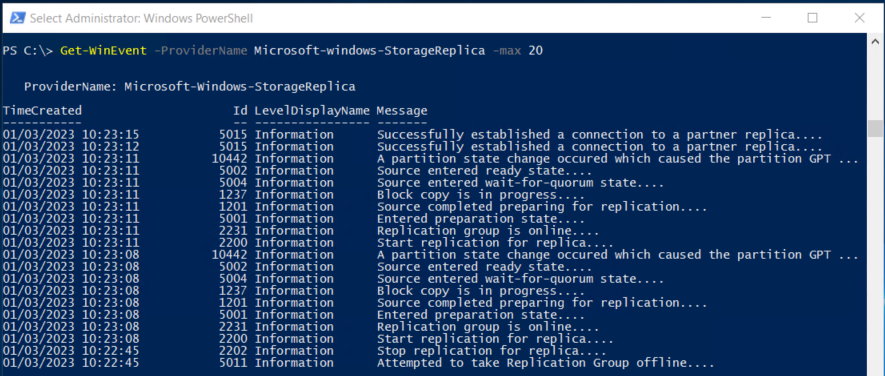
    In this case, the replication is not working and there are no other issues pointing to what could be the problem. In my case the solution was to restart the Storage Replica service from the services.msc. After this, I ran the Get-WinEvent command again and it was replicating again.


  • Server Manager refresh failed error

    Server Manager refresh failed error

    When opening Server Manager on the server, in the notifications you will see an error stating Refresh Failed.

    At this stage, you will not be able to add any features to the server and you will not be able to add or remove windows features.

    A pop-up about collecting inventory data and a refresh error saying “Configuration refresh failed with the following error: Invalid class” will show.

    Before proceeding you can take a backup of this by using the command below
    winmgmt /backup %computername%_MM_DD_YEAR.WMI_backup

    To fix the problem you would need to do the following in a command prompt as Administrator.

    winmgmt /verifyrepository
    winmgmt /salvagerepository
    winmgmt /resetrepository

    This will resolve the problem and when you relaunch the Server Manager, you will be able to add the features with no issues.

  • Install Module with PowerShell: NuGet Unable to download, check your internet connection

    Install Module with PowerShell: NuGet Unable to download, check your internet connection

    While installing the NuGet PowerShell module, you will get the following error

    WARNING: MSG:UnableToDownload «https://go.microsoft.com/fwlink/?LinkID=627338&clcid=0x409» «»
    WARNING: Unable to download the list of available providers. Check your internet connection.
    WARNING: Unable to download from URI 'https://go.microsoft.com/fwlink/?LinkID=627338&clcid=0x409' to ''.
    Install-PackageProvider : No match was found for the specified search criteria for the provider 'NuGet'. The package provider requires 'PackageManagement' and 'Provider' tags. Please check if the specified package has the tags.
    At line:1 char:1
    + Install-PackageProvider -Name NuGet -MinimumVersion 2.8.5.201 -Force
    + ~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~
    + CategoryInfo : InvalidArgument: (Microsoft.Power...PackageProvider:InstallPackageProvider) [Install-PackageProvider], Exception
    + FullyQualifiedErrorId : NoMatchFoundForProvider,Microsoft.PowerShell.PackageManagement.Cmdlets.InstallPackageProvider

    To resolve the problem open a PowerShell window as Administrator and enter the following command.
    [Net.ServicePointManager]::SecurityProtocol = [Net.SecurityProtocolType]::Tls12

    This will resolve the problem temporarily as if you would run the command again, it will still prompt the same problem. To resolve the issue permanently, you need to update the registry by running the below command to update the registry.

    Set-ItemProperty -Path 'HKLM:\SOFTWARE\Wow6432Node\Microsoft\.NetFramework\v4.0.30319' -Name 'SchUseStrongCrypto' -Value '1' -Type DWord

    Set-ItemProperty -Path 'HKLM:\SOFTWARE\Microsoft\.NetFramework\v4.0.30319' -Name 'SchUseStrongCrypto' -Value '1' -Type DWord

    Close all PowerShell windows and try again with the following command to confirm that the protocol has been updated.

    [Net.ServicePointManager]::SecurityProtocol