Category: Microsoft

  • WSUS Not working on Windows Server 2025

    WSUS Not working on Windows Server 2025

    When setting up WSUS on a Windows Server 2025, one might encounter issues with the update of the repository, and the server will never synchronise.

    After looking at the logs, which can be found in the C:\Windows\UpdateLog.log one would see timeout errors.

    First things to check are the firewall and internet access of the server. The other reason why the synchronization would fail it would be due to the security defaults of Windows Server 2025, where TLS and SSL, which are disabled by default.

    For WSUS to work, one needs to enable these protocols. To enable them, one can use applications such as IIS Crypto, which can be downloaded from the link below.

    https://www.nartac.com/Products/IISCrypto/

    After enabling TLS and SSL, reboot the server. After logging in, try to synchronize the WSUS, and it should be working.

  • Disable MFA requirement in Microsoft 365 for specific users

    Disable MFA requirement in Microsoft 365 for specific users

    We would require a specific user or a migration process to have MFA disabled. Although it’s not suggested due to security reasons, we might be forced to have it disabled.

    If you disable the Multifactor authentication from the Multi-factor authentication in the Active Users, it will not matter as the system will still be enabled.

    Before proceeding, a group should be created for example MFA Excluded and put the users needed in the group.

    For this and the new portal changes Microsoft have done, you need to get into the Entra ID admin portal.

    https://entra.microsoft.com

    Click on Protection from the side pane and click on Authentication Methods.

    Click on Policies and click on Microsoft Authenticator.

    Click on the Exclude tab and add the group that was created earlier.

    This should allow you to use an account without MFA.

  • Pre-Provision a user’s OneDrive in Microsoft 365 using PowerShell

    Pre-Provision a user’s OneDrive in Microsoft 365 using PowerShell

    When a new account is created in Microsoft 365, its OneDrive is not provisioned, which the user must do. If you needed to pre-provision it for the user, you would need to log in with every user or use the below method to pre-provision it using PowerShell. Usually, this is done to pre-fill the OneDrive of a user with startup data and folder structure as well as it is needed to be provisioned for a migration process.

    A requirement for this is to have the SharePoint Online Management Shell installed, which can be downloaded from the Microsoft site https://www.microsoft.com/en-US/download/details.aspx?id=35588&msockid=3765afd8b0d06ff03ce2baf8b1a76eb2.

    Once downloaded and installed, open a PowerShell window.

    Type the following command

    Connect-SPOService -Url <your admin sharepoint URL>

    The admin SharePoint URL is usually the domain -admin.sharepoint.com for example https://mydomain-admin.sharepoint.com

    Then you will need the following command to pre-provision the Onedrive.

    Request-SPOPersonalSite -UserEmails <email address of user>

    This will provision the OneDrive or the user.

  • How to connect to an AzureAD joined computer with Remote Desktop

    How to connect to an AzureAD joined computer with Remote Desktop

    When trying to connect using Remote Desktop Connection (RDP) to a computer which is AzureAD joined, one will not be successful as it will fail to connect. To successfully connect, one should first open the Remote Desktop Connection, enter the details of the devices and save the save your connection settings to a .rdp file.

    To do this, follow the instructions below.

    Open the Remote Desktop Connection program.
    Enter the IP Address or computer name to connect to.
    Click the Save As button at the bottom of the screen.
    Save it someplace convenient as we need to edit it.

    In the next part we will be editing the .rdp file we saved using notepad or any text editor.

    Go to the end of the file, add the following lines:

    enablecredsspsupport:i:0
    authentication level:i:2

    Save the file and close.

    Now, double clicking the modified .rdp file and login using the format:

    AzureAD\YourFullUsername

    You will be able to remote connect to the machine.

  • Microsoft 365 online archive never starts

    Microsoft 365 online archive never starts

    When having a user mailbox, you enable the online archive mailbox and set the archive policy, but the emails never move from the user mailbox to the online archive. You run the full crawl with PowerShell but nothing happens.

    The problem could be that the Retention Hold is enabled. This can be fixed by running the below.

    Get-Mailbox "<email address of user>" | Select RetentionHoldEnabled

    This will show if the feature is enabled. Run the following command to remove the Retention Hold flag.

    Set-Mailbox "<email address of user>" -RetentionHoldEnabled $false

    Once this is complete, run the following command to re-run the job.

    Start-ManagedFolderAssistant -Identity "<email address of user>" -FullCrawl

    After some time you should see the archive being populated.

  • Fix Remote server returned ‘550 5.7.520 Access denied, Your organization does not allow external forwarding

    Fix Remote server returned ‘550 5.7.520 Access denied, Your organization does not allow external forwarding

    This is a security feature from Microsoft 365 where it will block emails from being forwarded outside the tenant. If you get such a message, this means that the recipient has forwarding set outside its tenant. To allow this feature, follow the below guide.

    Open the Office 365 Admin Center and click on Security.

    Under Email & Collaboration, click on Policies & Rules.

    Click on Threat Policies.

    Click on Anti-Spam under Policies.

    Click on Anti-spam outbound policy (Default).
    Scroll down and click on Edit protection settings.
    Under Forwarding Rules, change the Automatic forwarding rules from Automatic – System-controlled to On – Forwarding is enabled.
    Click on Save.
  • Changing Timezone from command line

    Changing Timezone from command line

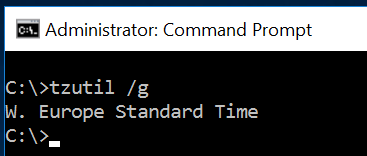
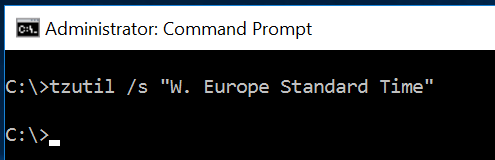
    It would be the case that you would need to change the time zone on the server but from the Time & Date option, it would be greyed out due to policy. There is a workaround for changing the timezone using the Command Prompt as Administrator.

    Type tzutil /g to get the current time zone.

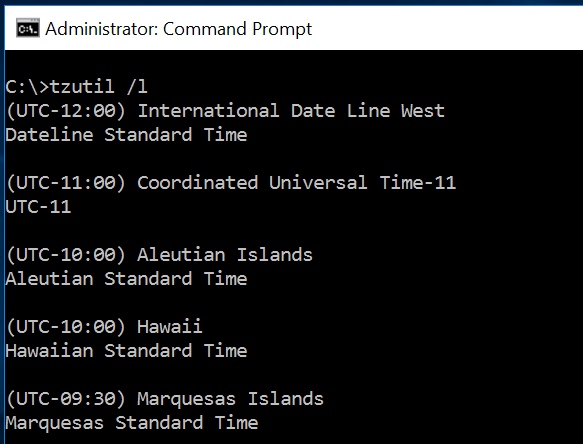
    Type tzutil /l to list the available time zones.

    Use tzutil /s "<timezone name>" to change the desired timezone.


  • Fix Remote Desktop Licensing Mode is not configured

    Fix Remote Desktop Licensing Mode is not configured

    Having fully installed Remote Desktop Services (RDS) on a server with the RD Connection Broker and RDS licensing set per user and everything is working with a valid license.

    After some time you notice a popup when you connect saying,

    Remote Desktop licensing mode is not configured
    Remote Desktop Services will stop working in 104 days. On the RD Connection Broker server, use Server Manager to specify the Remote Desktop licensing mode and the license server.
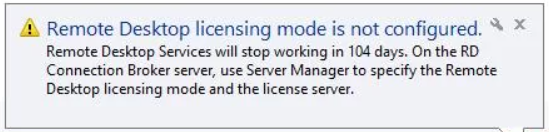
    When you open the RD Licensing Diagnoser, you will be prompted with an error saying, The licensing mode for the Remote Desktop Session Host server is not configured.

    From the Server Manager under Configure the Deployment and RD licensing, all seem to be configured well.
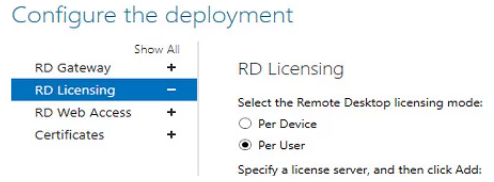
    Open a PowerShell as Administrator on the server and run the following command

    $obj = gwmi -namespace "Root/CIMV2/TerminalServices" Win32_TerminalServiceSetting
    $obj.GetSpecifiedLicenseServerList()

    This will show a parameter called SpecifiedLicenseServerList which would be empty as below.

    To populate the parameter, use the following command

    $obj.SetSpecifiedLicenseServerList("<full fqdn server name>")

    After this is done, the RD Licensing Diagnoser parameter should not report any errors. It is suggested to restart the server after this change.

    Alternatively, one could do this with registry with the following PowerShell script

    # Specify the RDS licensing type: 2 - Per Device CAL, 4 - Per User CAL
    $RDSCALMode = 4
    $RDSlicServer = "<server full fqdn name>"
    # Set the server name and type of licensing in the registry
    New-Item "HKLM:\SYSTEM\CurrentControlSet\Services\TermService\Parameters\LicenseServers"
    New-ItemProperty "HKLM:\SYSTEM\CurrentControlSet\Services\TermService\Parameters\LicenseServers" -Name SpecifiedLicenseServers -Value $RDSlicServer -PropertyType "MultiString"
    Set-ItemProperty "HKLM:\SYSTEM\CurrentControlSet\Control\Terminal Server\RCM\Licensing Core\" -Name "LicensingMode" -Value $RDSCALMode

  • Install Windows 10 or 11 with a local user

    Install Windows 10 or 11 with a local user

    On Windows 10 and Windows 11, you will be forced to log in the machine with a Microsoft Account. There is a way to bypass this and use only a local account without having to create a Microsoft Account to set it up.

    Once you get to this screen, press Shift and F10

    This will open a Command Prompt. Enter ipconfig /release and press the Enter key. This will release the IP address and disconnect the computer from the internet.

    Close the Command Prompt window. Go back from the arrow on the top left and you will be asked to create a local user.

    Like this you will not be forced to log in with a Microsoft Account.


  • Fix: Storage Replica warning Events 10448 Storage Replica has failed an application IO

    Fix: Storage Replica warning Events 10448 Storage Replica has failed an application IO

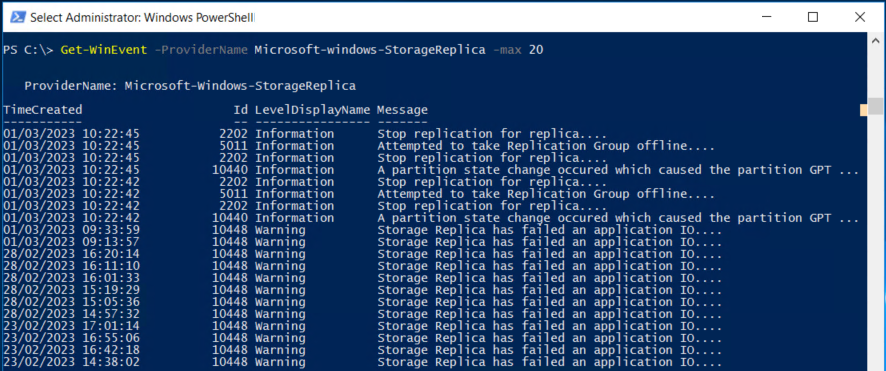
    When checking the logs of the Storage Replica on a Windows Server 2016, 2019 or 2022, using the below command, you get the error saying that Storage Replica has failed an application IO.

    Get-WinEvent -ProviderName Microsoft-Windows-StorageReplica -max 20

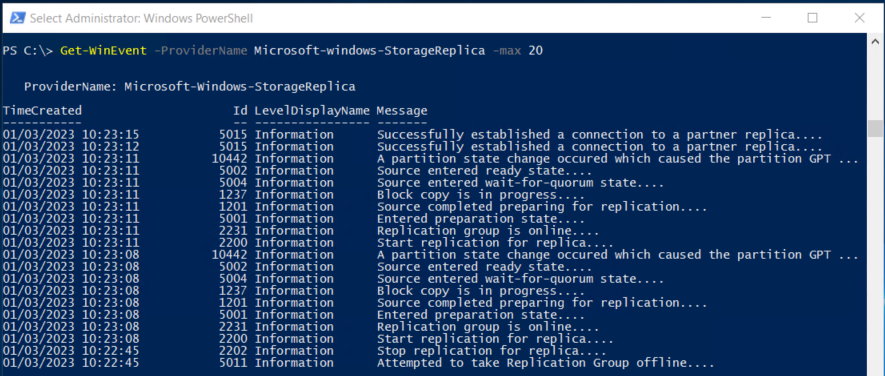
    In this case, the replication is not working and there are no other issues pointing to what could be the problem. In my case the solution was to restart the Storage Replica service from the services.msc. After this, I ran the Get-WinEvent command again and it was replicating again.